Use case
Redact secrets from screenshots for security reviews
Capture the relevant configuration or log, redact secrets and inspect the export before sending it to reviewers. Record what you removed and how access will end. Screenshots support a review but do not provide tamper-evident evidence.
Capture
Capture the screen under review, including the config panel or log lines that matter.
Redact
For local-only work, manually cover secrets with the public redactor. On an already-synced capture, the paid cloud editor can suggest likely secrets for review. Use opaque blackout and verify the export.
Share
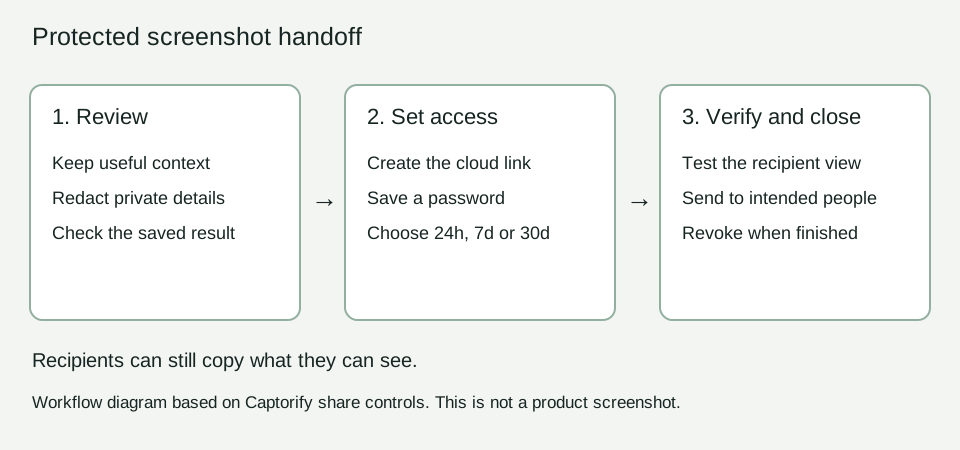
Send the checked file through your approved channel, or use a paid password-protected link with an expiry. Revoke the link when the review closes.
The security screenshot risk
A screenshot taken for a security review can quietly expose API keys, access tokens, internal hostnames, and account identifiers sitting in a config screen, a network panel, or a log. Captorify helps a reviewer find those secrets, remove them permanently from the pixels, and share the result with controls instead of pasting a raw image into a thread.
How teams use it
Decide whether the original can be uploaded before capture. Turn off "Sync captures to cloud" or use a native browser capture for local work, then use the public manual redactor. The paid editor and its suggestions operate on already-synced captures. Review the final export either way.
OCR and pattern checks
OCR can help identify visible secret-like text, but it can miss characters and is not a security clearance. The free public OCR tool processes a local image; the paid cloud editor performs local recognition on a synced capture. The public redactor also offers local English OCR suggestions. Review and explicitly accept suggested regions before applying redaction.
- The free public redactor offers manual blackout and local English OCR suggestions that you review and accept. Editing already-synced captures in the cloud editor requires a paid plan.
- Suggested redaction is a review step, so you confirm each match rather than trusting a blind sweep.
- Reopen the exported image and inspect all regions. OCR is a supplementary check and cannot prove that no secret remains.
Limits of Captorify
Captorify makes a screenshot safer to share, but it is not a chain-of-custody tool. Blackout removes the underlying content, while blur and pixelate are baked in yet can in principle be reversible. The output is a cleaned image, not signed or tamper-evident security evidence, so pair it with your own controls when a review demands a formal record.
Record the review decision, not just the screenshot
Use the worksheet to record why the screenshot is needed, who will receive it, what was removed and when access should end.
The completed example shows how a reviewer records the redacted regions and final-file check. For your own review, record who checked the export and what was approved.
# Screenshot security review worksheet

Review owner: [name or team]
System and purpose: [the task this screenshot supports]
Data classification: [your organization's classification]
Recipient group: [specific people or team]
Required evidence: [what must remain visible]
Information removed: [identifiers, credentials, customer data, browser chrome]
Redaction method: [opaque replacement pixels in a newly encoded export]
Export verification: [reviewer, date, filename, result]
Sharing control: [attachment, authenticated workspace or protected expiring link]
Access end date: [date]
Revocation owner: [person or team]
Retention decision: [where checked copies may remain]
Exception or follow-up: [anything requiring human review]