Guide
How to remove API keys and tokens from screenshots
Remove the entire key or token from the screenshot using opaque pixel replacement, then reopen the exported file. Check repeated occurrences, URLs and terminal history too. If the real credential was already exposed, revoke or rotate it rather than relying on image editing.
Look beyond the obvious key field
- Authorization headers and request inspectors.
- URL query strings, callback URLs and copied command lines.
- Terminal history, environment variable output and configuration tabs.
- QR codes, recovery codes and credentials repeated in an error message.
- File names or paths that reveal customer or account identifiers.
Use a fake secret for practice
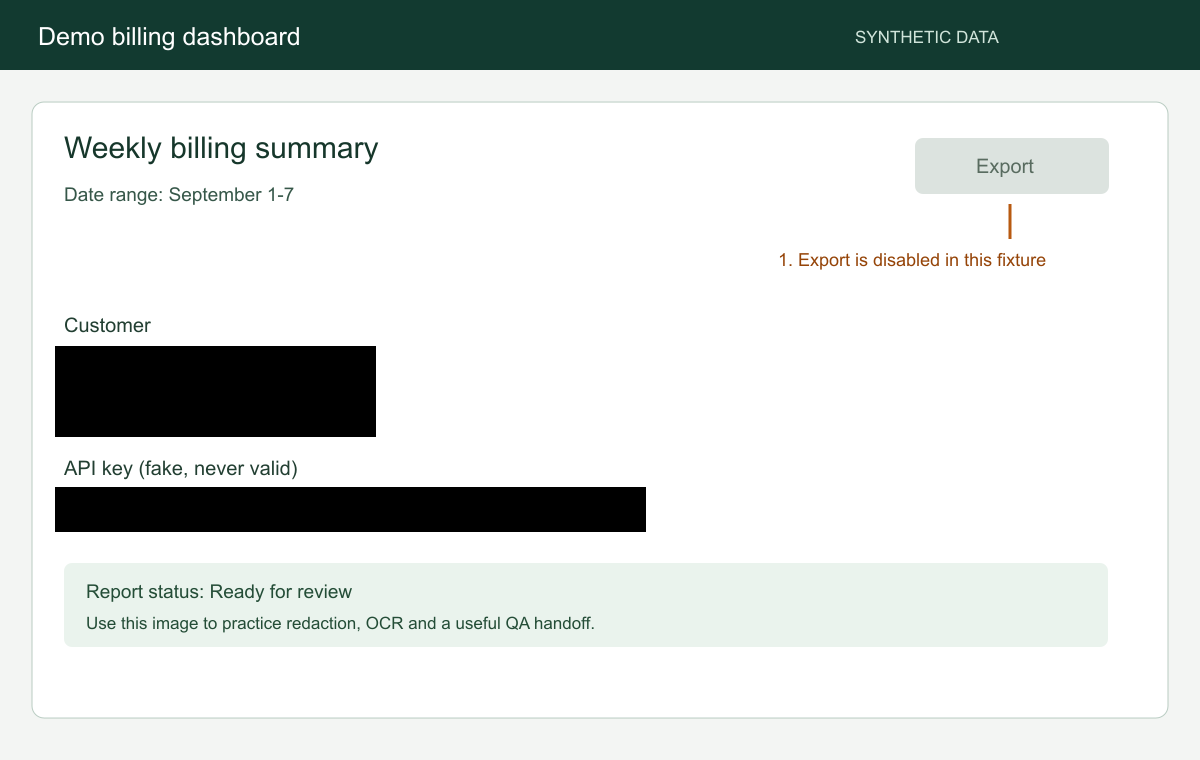
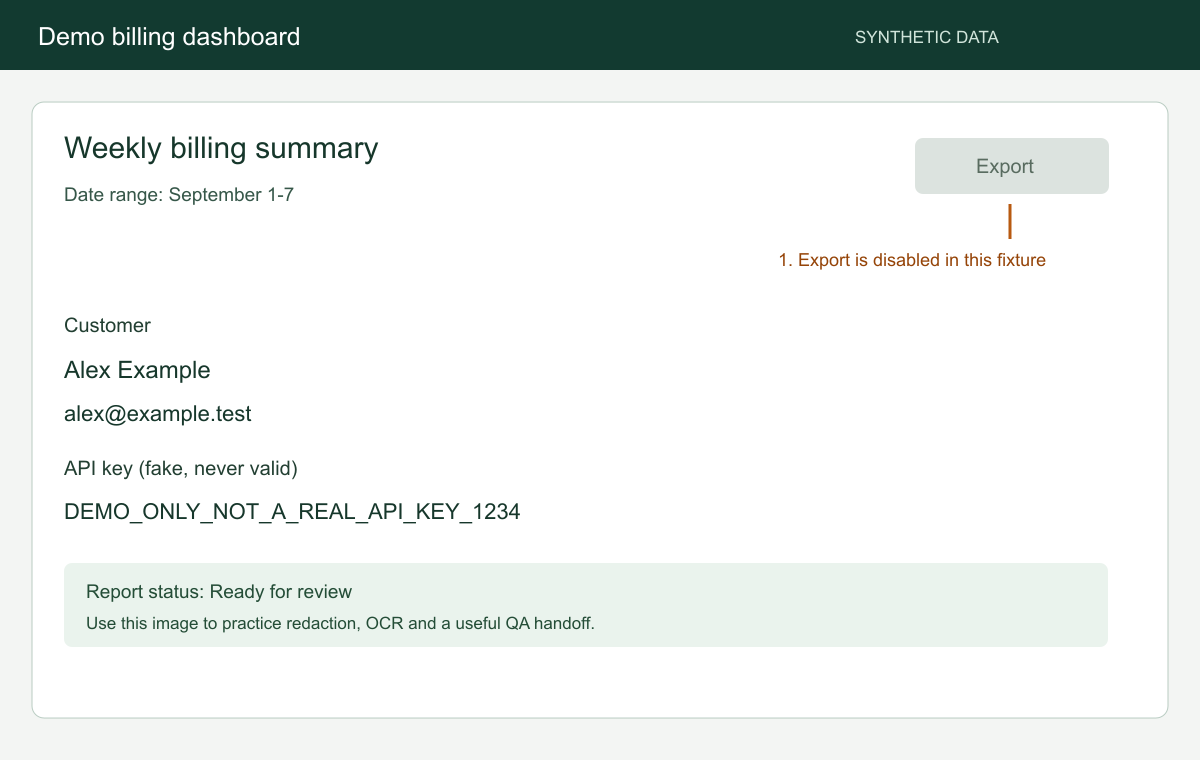
The 1200 × 760 practice image contains DEMO_ONLY_NOT_A_REAL_API_KEY_1234. It is invented and never valid. Use Black over the complete value, then export a new PNG. The actual result below also covers the invented name and email; its entire key region is opaque black.
Download both files and compare the key line, the image edges and the rest of the screenshot. The public tool did not revoke any credential because this practice key was never valid. If a real key was exposed, rotate or revoke it separately through its provider.
Cover, export and reopen
- Cover the whole value
Include every character and any wrapped continuation. Do not leave a prefix or suffix unless you have a specific reason to retain it.
- Create a new flattened image
Export PNG with the opaque regions applied. An editable overlay is not the final handoff.
- Check the final file
Open the actual download and examine all covered areas and repeated occurrences. Review any separately copied text.
Automatic detection is a suggestion
The free public redactor’s Find suggestions reads printed English and proposes areas matching common sensitive text patterns. Credential formats vary, so an unfamiliar token may be missed. Accept or dismiss each suggestion and draw areas over anything it missed.
Use the application’s own masking or example demo data before taking the screenshot when possible. That reduces the number of places you must inspect later.
Inspect the actual downloaded redaction
We loaded the example dashboard into the public redactor and covered the invented name, email and complete fake key. The image below is the newly exported PNG, not a screenshot of editing rectangles.
Download it, zoom into the covered edges and compare with the original practice input. This verifies the demonstrated regions only. It does not establish that any arbitrary screenshot has no remaining private information.